
Copilot for RIAs: Work vs. Web + Data Privacy (2026)

For your RIA, use work-grounded Microsoft Copilot for approved internal information and enterprise-protected web chat for public research; your sign-in, product, and settings determine privacy protections. You gain useful support from an AI assistant when you choose the right information for the task and keep client data within your firm’s approved controls.
You should treat data access and data protection as separate decisions. Work grounding gives Copilot access to permitted business content. Enterprise data protection governs how your information is handled in covered business experiences, including eligible web-grounded chat.
For RIAs, that distinction helps you prepare meeting materials and research public topics while keeping clear records of what staff used and reviewed. Your starting point is an approved business account, well-managed permissions, and defined rules for client information.
What Is the Difference Between Work and Web?

You use work grounding to draw on permitted business content and web grounding to draw on public information. Files you supply and enabled tools also shape what Copilot uses.
Comparison | Copilot for Work | Copilot for Web |
Main grounding | Permitted work content | Public web content |
Broad Microsoft 365 access | With eligible entitlement | Through added content or features |
Supplied files | Supported where available | Supported where available |
Enterprise protection | Covered business experience | Covered business experience |
Advisory use | Internal meeting preparation | Public-topic research |
How Work Mode Uses Microsoft Graph and Existing Permissions
With Copilot work mode, you receive answers grounded in Microsoft 365 data you have permission to access. Microsoft Graph connects relevant content, such as documents and email, to the business context behind your request.
Your permissions set the access boundary. If a confidential folder is shared too broadly, an authorized user’s Copilot request could surface its contents. You should therefore include permission reviews in your cloud security controls for financial advisors.
You also need a supported connection or supplied content before using information held in an external system. A Copilot license alone does not establish access to your CRM or financial planning platform.
How Web Mode Uses Public Sources and Supplied Content
In Copilot web mode, you use public information retrieved through web search, including Bing-powered search where enabled. You might ask for current public guidance on retirement contribution rules or an explanation of a published economic release.
You also influence the answer through your prompt and anything you attach. Uploading a client statement introduces client information into that conversation, even when work grounding is off.
Before submitting a request, check the selected files and any open-app context available to Copilot. Treat every attachment as an intentional disclosure to the approved service.
Why Web Mode Is Not the Same as Consumer Copilot
You should distinguish enterprise-protected web chat from consumer Copilot by checking the account and service you are using. A work account in a covered Microsoft 365 Copilot Chat experience receives business protections that differ from those attached to personal-account use.
Your browser alone tells you little about that distinction. Both business and consumer experiences run in browsers, and both offer web-based answers.
Require staff to confirm the firm-approved account before entering work information. Include that check in your remote work security procedures, especially on devices used for personal browsing.
What Actually Determines Copilot’s Data Privacy Protections?
Your privacy protections follow the covered service, signed-in account, contractual terms, and enabled features. The grounding control tells you which information Copilot uses to prepare an answer.
When Does Enterprise Data Protection Apply?
You receive enterprise data protection (EDP) when using covered Microsoft Copilot and Microsoft Copilot Chat organizational experiences. Your use is covered by Microsoft’s Data Protection Addendum and Product Terms, with Microsoft acting as a data processor.
Check that you are signed in through your firm’s Microsoft Entra work account. Then confirm the product and protection indicators available in that experience with your administrator.
Treat EDP as part of your data protection program. You still need policies governing sensitive information and proprietary work information, including who is allowed to submit each type.
Are Prompts, Responses, and Files Used to Train AI Models?
In covered business experiences, you receive protection against your work content being used to train foundation models. Your prompts, responses, and Microsoft Graph content are excluded from foundation-model training; supplied files receive the protections applicable to that covered experience.
You should separate that training commitment from retention. Your interactions may be retained and available through applicable compliance tools, subject to the service and your configuration.
Document those settings before approving sensitive workflows. Your data encryption requirements should also cover stored files and exported answers.
How Can Web Search, Uploads, and Agents Affect Data Handling?
You need to assess each enabled route through which Copilot processes information. Web grounding generates search queries for the search service, which has distinct data-handling terms. Avoid assuming every step of a conversation stays inside your Microsoft 365 tenant.
Use these checks before approving a workflow:
Web search: Keep client identifiers and account details out of research prompts.
Uploads: Confirm the file’s classification and the user’s authority to submit it.
Agents: Review connected systems, permissions, and publisher terms.
Actions: Require approval before a tool sends information or changes a record.
Review any third-party model or service choices under the terms that apply to your deployment.
Which License and Sign-In Does Your Firm Need?
You need an eligible Microsoft 365 work account and the entitlement required for your intended Copilot features. Your subscription, assigned license, and administrator settings determine access.
Business Standard, Business Premium, and Copilot Licensing
You should check Business Standard or Business Premium separately from the Copilot entitlement assigned to each user. These Microsoft 365 subscriptions provide a foundation for eligible business Copilot offerings; access to broadly work-grounded features requires the appropriate paid entitlement.
Your Copilot licensing options include different levels of chat and Microsoft 365 integration. When buying, confirm the exact offering available to your organization and the features included.
You will encounter the older name “Copilot for Microsoft 365” alongside Microsoft 365 Copilot terminology. Record the actual subscription and assigned service plans in your technology roadmap, so procurement and compliance use the same description.
Where to Find Work and Web Options
In the Microsoft 365 Copilot app, check the grounding controls shown in your account. Your interface might differ from screenshots that show a work/web toggle.
In the updated experience, the Work IQ button replaces separate Work and Web tabs. You use that control to determine whether Copilot references your work data.
You should also inspect the conversation’s data-source controls. Where available, Change data sources lets you turn reference sources on or off. Confirm these selections before handling client-related material.
What to Check When Work-Grounded Answers Are Unavailable
Start with your account and assigned entitlement. Confirm that you are using the firm’s work account in the intended tenant, then ask your administrator to check the user’s license and enabled services.
Next, check the app and applicable Copilot deployment requirements. Your administrator should also review grounding settings and any policy restrictions.
Test with a harmless document you already have permission to open. If Copilot fails to find it, investigate that specific access path before expanding permissions. Keep restricted client folders closed while troubleshooting.
What Should RIAs Secure Before Enabling Copilot?
You should secure permissions, identity, and information governance before enabling sensitive Copilot workflows. For RIA firms, preparation starts with the Microsoft 365 tenant and extends to staff behavior.
Review SharePoint, OneDrive, and User Access for Oversharing
Begin with locations containing client records or other sensitive information. Review SharePoint membership, OneDrive sharing links, guest accounts, and inherited access.
Your review should identify broad internal groups and sharing links that outlast their business purpose. Microsoft’s governance guidance confirms that Copilot uses work information the user already has permission to access.
Assign an owner to each sensitive location and record access decisions. Include that evidence in your RIA cybersecurity readiness checks, then retest access using representative staff accounts.
Configure Identity, Sensitivity Labels, and Data Loss Prevention
Protect your sign-ins with multi-factor authentication and apply Conditional Access controls supported by your licenses. Limit administrative privileges and define device requirements for sensitive work.
Use sensitivity labels to classify information and apply supported protections. Configure data loss prevention (DLP) for the locations and Copilot scenarios covered by your licensing.
Test the result with sample content before rollout. A classification label’s effect depends on its settings; document whether it applies encryption, access restrictions, or other controls.
You can draw on Secure Wealth IT’s financial-industry focus for Microsoft 365 administration and access controls while keeping approval decisions with your firm.
Define Approved Uses, Retention, and Audit Evidence With Compliance
Put your AI rules into your written information security policy. Define permitted accounts, approved information types, prohibited uses, and required review before client delivery.
Work with compliance to decide which interactions and outputs require retention. Confirm that your tooling captures the required records and that authorized staff are able to retrieve them.
For an SEC-registered RIA, connect these decisions to applicable recordkeeping duties and Regulation S-P safeguards. Add FINRA requirements where your business operates as a broker-dealer. Keep training acknowledgments and control-test results with your audit evidence.
Which Advisory Tasks Belong in Each Mode?

Use Copilot for Work for approved internal preparation and Copilot for Web for public research with client details removed. Choose the grounding based on the information needed to complete the task.
Prepare Client Meeting Briefs Using Approved Internal Sources
With work grounding enabled, ask Copilot to summarize specific, approved Microsoft 365 data. Name the documents or meeting records you want included and request citations for each factual statement.
For example, you might ask: “Using the approved meeting notes and planning summary, draft an agenda. Flag missing information and unresolved questions.”
Verify that each cited item belongs to the correct household and reflects the latest approved information. Keep account balances and planning assumptions tied to their authoritative records. Treat proprietary work information in the resulting brief under your existing access rules.
Research Public Topics Without Exposing Client Details
Use enterprise-protected web chat to explore public topics such as published tax guidance or market commentary. Give Copilot the public question and any relevant jurisdiction or date.
For a retirement-rule question, ask for the current rule and links to official government material. Leave out the client’s name, account number, and full financial profile.
You should also remove identifying combinations of facts. An employer name paired with a detailed equity position may reveal more than your research needs. Ask the general question first, then apply verified findings within your approved planning process.
Verify Sources and Review Drafts Before Client Use
Review every factual claim before using an answer with a client. Open the cited material and check its date, jurisdiction, and support for the statement.
For calculations, reconcile inputs and results against your approved financial tools. For client-facing language, check disclosures and any claims about performance or likely outcomes.
Preserve the approved version and evidence of required review under your recordkeeping procedures. You should also include these checks in staff cybersecurity and compliance training, so users know when to stop and escalate an uncertain result.
Choose the Right Data Source and Verify the Protections
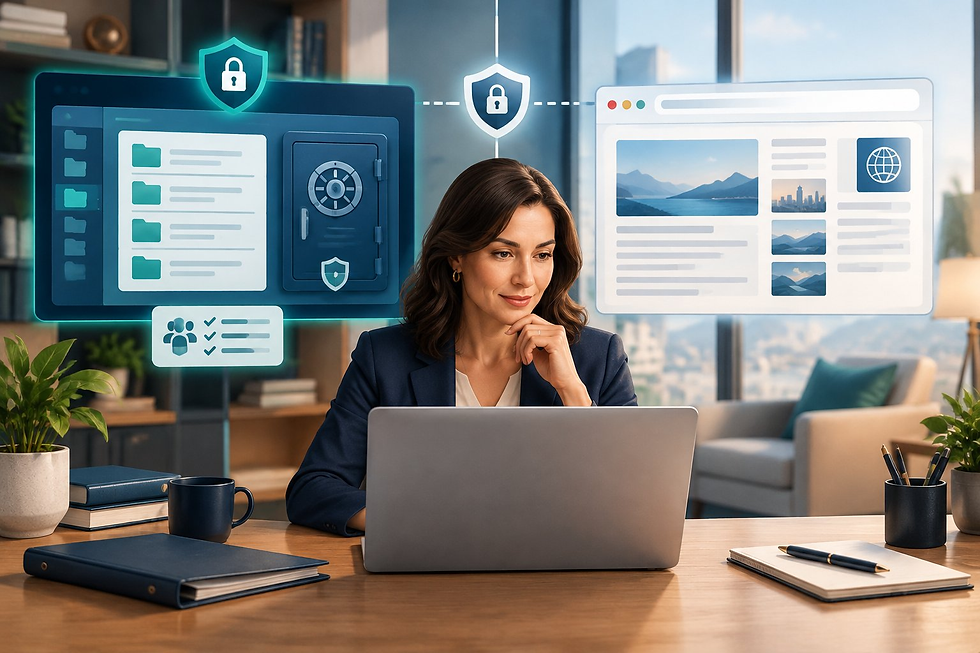
Your next step is to pair each approved advisory task with its permitted information and verified protection settings. In Microsoft 365 Copilot, confirm the work account, entitlement, grounding controls, and any connected tools before introducing client data.
For RIAs, a controlled rollout also needs tested permissions and human review. Keep enterprise data protection documented alongside retention settings and staff instructions, then begin with a limited set of approved workflows.
If you want help reviewing that foundation, you can request Secure Wealth IT’s free compliance readiness assessment at (704) 769-3663. Use it to identify gaps in Microsoft 365 access controls, staff training, and audit-ready documentation before expanding your rollout.
Next Steps for Your RIA or Broker-Dealer Firm
Secure Wealth IT helps Registered Investment Advisors, broker-dealers, and financial advisors stay secure, compliant, and audit-ready. Explore these free tools and resources:
Free Financial Calculators: calculator.securewealthit.com
Compliance Self-Assessment Tool: regulations.securewealthit.com
Resource Library: Browse free RIA and broker-dealer guides.
Watch on YouTube: Secure Wealth IT YouTube channel.
Talk to a Specialist: Schedule a free consultation.
For more information about this topic, visit us at https://www.securewealthit.com


Comments