
Managing Texting & SMS Compliance Risks for RIAs: A Guide


You manage texting and SMS compliance risks for your RIA by using approved channels, collecting appropriate consent, capturing required records, and documenting message reviews. These controls let you offer convenient business text messaging while keeping client conversations available for oversight and protecting private information.
Your SMS compliance duties come from several places. Securities rules govern required records and supervision. Consent laws govern certain texts you send, while carrier standards govern access to messaging networks.
Your starting point is a clear inventory: who texts clients, which numbers they use, what they discuss, and where those conversations are saved. With that information, you can address specific gaps in RIA compliance without making every client exchange harder.
Which Texting Rules Apply to Your Firm?
Your applicable texting rules follow your firm’s registration, message content, and sending method. You need separate checks for securities records, consent requirements, and carrier acceptance.
What Does SEC Rule 204-2 Require Firms to Preserve?
If your firm is SEC-registered, SEC Rule 204-2 requires you to preserve specified written communications sent or received. Covered subjects include investment recommendations or advice, securities orders, certain performance information, and the receipt or movement of client funds or securities.
You should classify messages by their content. A scheduling-only text does not automatically become a required record under Rule 204-2 merely because you exchanged it with a client.
Your firm’s policy can require broader capture to reduce classification errors. Document that choice as a firm control, with your CCO or counsel defining the legal retention scope.
When Do FINRA Rules Apply to Advisors?
You need to assess FINRA rules when your firm is a FINRA member broker-dealer or your activities fall under a member firm’s supervision. An independent RIA’s SEC registration alone does not create FINRA membership.
For brokerage activities, your review should address FINRA Rule 3110 on supervision and Rule 4511 on books and records, alongside applicable SEC broker-dealer requirements. If you operate a dual registrant, identify which entity and business activity each communication involves.
Give your advisors clear instructions for conversations that cross advisory and brokerage services. Your approved process should preserve the relevant records without requiring employees to resolve legal categories during a client exchange.
How Do Securities Rules Differ from TCPA and Carrier Requirements?
You satisfy different obligations through each framework. The Telephone Consumer Protection Act (TCPA) and Federal Communications Commission (FCC) rules address unwanted communications, including consent and opt-outs where applicable.
Your securities obligations address required records and oversight. CTIA guidance and carrier policies add messaging standards that affect delivery.
Keep separate approval checks for these duties. A carrier-approved campaign still needs an appropriate consent process and a verified recordkeeping workflow.
What Consent Do You Need Before Texting Clients?
You need consent that fits the message’s purpose, sending technology, and applicable law. Your client relationship alone does not establish permission for every SMS campaign.
Distinguishing Service Messages from SMS Marketing
You should separate service communications from SMS marketing before drafting messages. Appointment confirmations and requested account-service updates serve different purposes from promotional outreach about your advisory services.
Keep your templates focused on their approved purpose. Adding a sales pitch to a service reminder changes the consent analysis.
Give your staff examples of approved content for each category. Have your CCO review market commentary, webinar invitations, and prospect follow-ups because their wording and purpose affect how you should treat them.
When Is Prior Express Written Consent Required?
You need prior express written consent for advertising or telemarketing texts sent using technology covered by the TCPA’s automated-call restrictions, subject to applicable exceptions. Your analysis should also address do-not-call rules and state laws, which have their own scope.
For covered informational texts, prior express consent is the relevant federal standard. Obtain legal review of your sending system and use case before deciding which consent standard applies.
When you collect express written consent, use clear disclosures that identify your firm and explain the authorized messages. Include required language about automated messaging and consent not being a condition of purchase when applicable; an electronic signature can support written consent.
How Should Firms Document Opt-Ins and Honor Revocations?
Your SMS opt-in record should connect the recipient’s number to the exact disclosure they accepted. Save the date, collection method, consent wording, and evidence of the affirmative action.
Use double opt-in when you want added confirmation that the person controls the number. Treat it as an added safeguard unless a specific requirement makes it mandatory.
Honor revocations through your approved process, including reasonable requests made outside a STOP reply. Suppress further messages within applicable deadlines, preserve the request, and confirm that connected systems apply the change.
What Should Your Written Texting Policy Cover?
Your written policy should give employees clear instructions for approved texting and exceptions. Connect each rule to an owner and a process your team can follow.
Define Approved Channels, Message Types, and Employee Responsibilities
List the platforms and business numbers your employees are authorized to use. State which messages each channel supports, including any limits on recommendations, account instructions, or promotional content.
Assign responsibility for approving users, checking archive capture, reviewing messages, and resolving exceptions. Your advisors should know where to report off-channel communications.
Set review and escalation expectations without implying that every RIA message requires advance approval. Your supervision process should reflect your business, applicable rules, and identified risks.
Set Conditions for Personal Devices and Business Numbers
You can permit personal devices when your approved setup supports the required security, capture, and oversight. Device ownership alone does not determine whether business text messaging is acceptable.
Your bring-your-own-device policy should explain enrollment, supported apps, business-record access, and the separation of personal information. Obtain employee acknowledgment of monitoring and device-management conditions.
Define control of business numbers and the process for transferring them. Include what happens when an employee changes devices, leaves your firm, or withdraws permission for required management controls.
Handle Client-Initiated Texts on Unapproved Channels
Give your employees an approved response for redirecting clients who contact personal numbers or unapproved apps. Keep that response focused on moving the conversation to an authorized channel.
Require prompt reporting and preservation of the original exchange under your exception process. Your compliance team should decide how to collect the record and document corrective action.
Discourage continued business discussion while the exchange remains outside your controls. For urgent client instructions, use your established verification and escalation procedures.
How Should Business Text Messages Be Captured and Retained?
Your text message archiving process should preserve required communications automatically and make them retrievable. Verify coverage for each approved channel before employees begin client texting.
Match Capture Coverage to SMS, iMessage, RCS, and Messaging Apps
Build a coverage list showing your approved devices, carriers, messaging formats, and capture methods. Treat SMS, MMS, iMessage, RCS, and app-based messaging as separate items to verify.
You should test supported configurations directly. A conversation’s appearance in the same phone app does not prove that every underlying message format follows the same capture path.
When evaluating RIA compliance technology such as Smarsh or Global Relay, ask for configuration-specific coverage. Your approval should identify supported operating systems and any settings employees must maintain.
Preserve Conversation Context, Attachments, and Metadata
Your archive needs enough information to reconstruct the exchange. Check message content, participants, timestamps, attachments, and the connection between inbound and outbound messages.
You can evaluate documented capture capabilities against that checklist. Smarsh’s mobile offering preserves messages, media, attachments, and metadata across supported channels, with coverage tied to its supported platforms and configurations.
Confirm how your selected solution handles reactions, group conversations, and changed or deleted content where supported. Keep original records and an audit trail for administrative actions.
Set Applicable Retention Periods, Legal Holds, and Retrieval Tests
You should map each required record category to its applicable retention rule. Under SEC Rule 204-2, many covered records carry a five-year retention period, with the calculation tied to the end of the fiscal year in which the last entry was made.
Your schedule must account for the specific record type, applicable accessibility conditions, and any additional state or broker-dealer requirements. Have your CCO approve the settings before applying automated deletion.
Suspend scheduled destruction when a legal hold applies. Test searches and exports using known conversations, then confirm that the production contains the full exchange and relevant attachments.
How Do You Evaluate a Business Texting Platform?

You should approve a business texting platform only after verifying the complete workflow from message delivery through retention and review. A familiar interface is useful, but your approval needs documented evidence of the controls behind it.
Separate Messaging Features from Archiving and Supervision
Evaluate sending features separately from recordkeeping controls. A shared inbox or searchable message history does not establish that your required retention settings are active.
Ask how your proposed configuration protects records, controls deletion, applies holds, and supports exports. Then check how reviewers receive and resolve flagged conversations.
If you use Smarsh or Global Relay alongside a messaging platform, define the responsibility of each component. Your implementation plan should name who monitors the connection and who responds when ingestion fails.
What Must Firms Verify Before Using Microsoft Teams SMS?
Before approving Microsoft Teams SMS, verify your current tenant’s eligibility and the requirements for your specific service. Check Teams Phone licensing, supported number types, geographic availability, and carrier registration.
Confirm support for the message formats and conversation types your clients use. Ask your Microsoft provider to demonstrate the exact workflow you plan to deploy.
Validate how those SMS records enter your retention and supervision systems. Your Microsoft 365 subscription or an existing Teams chat retention policy does not, by itself, establish that the SMS workflow meets your requirements.
Test Archive Integrations, Number Ownership, and Employee
Offboarding
Run an acceptance test that follows messages from the client’s phone into the archive. Include replies, attachments where supported, failed delivery, and a temporary connection outage.
Confirm that your firm controls business-number administration and has a documented transfer process. Record who is authorized to request changes or port numbers.
Test employee offboarding before relying on the process. You should be able to revoke access, preserve historical messages, and reassign client coverage without losing records or exposing them to unauthorized staff.
How Can Firms Protect Client Information in Text Conversations?
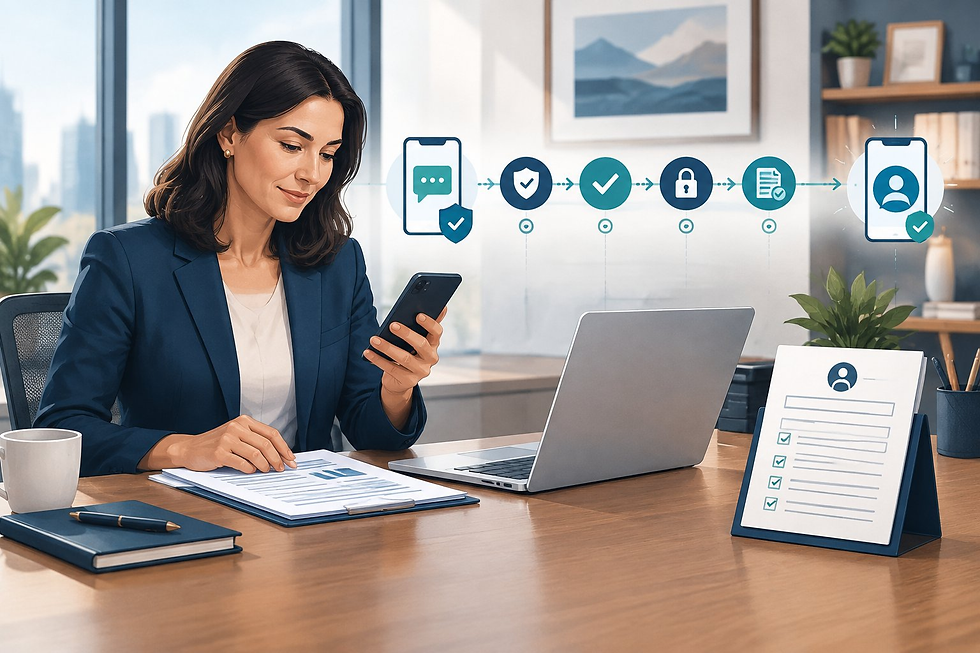
You protect client information by limiting text content and controlling access to the systems that handle it. Your safeguards should address the SEC’s Regulation S-P privacy rule where applicable, along with your broader security obligations.
Move Sensitive Documents and Instructions to Secure Channels
Use texts for approved coordination and direct clients to your secure portal for sensitive documents. Your policy should restrict account credentials, Social Security numbers, and other high-risk information in ordinary SMS.
For money movement or account changes, follow your established authentication procedures. A message arriving from a familiar number does not establish the sender’s identity.
Prepare short, approved wording that directs clients to your portal or known office number. Avoid including private account details in the redirection message.
Apply Access Controls, Device Management, and Remote Wipe
Require strong authentication for access to your business texting platform and archive. Limit administrative access and give reviewers only the permissions their roles require.
For managed devices, apply screen locks, supported software updates, and controls over local data storage. Review lock-screen previews because they expose message content without opening the app.
Use remote-wipe or selective-wipe capabilities where your device-management setup supports them. Preserve required records in the archive before removing business data, and explain personal-device boundaries to employees.
Prepare for Lost Devices, Smishing, and Data Exposure
Include texting systems in your incident response plan. Your staff should know how to report a lost phone, suspicious text, or accidental disclosure immediately.
For smishing, which is phishing by text, train employees to verify unusual requests through a known contact method. Capture relevant evidence and involve your security team before taking actions that erase useful information.
If data exposure occurs, assess containment and applicable notification duties with your CCO and counsel. Your response should address affected clients and vendors while reducing the risk of further data breaches and reputational damage.
What Do CTIA Guidelines and 10DLC Registration Require?
Your carrier-facing requirements include registering applicable messaging traffic and maintaining a clear, consent-based program. CTIA guidelines inform industry practices, while your provider and carriers apply specific operational requirements.
Register Applicable Brands and Campaigns for A2P Messaging
If you send application-to-person messages through a US 10-digit long code, verify your provider’s A2P 10DLC registration requirements before launch. A staff member typing each message does not automatically place platform-based traffic outside carrier registration rules.
Your registration process should use accurate legal business information and describe the intended messaging use. Keep your sample messages consistent with your real opt-in process and campaign purpose.
Confirm that the correct numbers are assigned to the approved campaign. Retain registration evidence and track changes that require an update.
Provide Clear Sender Identification, HELP, and STOP Instructions
Identify your firm clearly so recipients recognize who is contacting them. Configure HELP responses with usable support information and STOP handling that suppresses further messages as required.
Test these controls from outside your firm. Check both the recipient’s response and the resulting change in your sending system.
Your employees also need a route for processing opt-out requests received through other reasonable methods. Coordinate those requests across systems according to their scope and applicable requirements.
Apply Appropriate Disclosures, Sending Hours, and Frequency Controls
Your opt-in flow should explain message purpose and expected frequency. Include applicable disclosures such as “message and data rates may apply,” along with required terms and privacy information.
Set sending windows using the recipient’s local time and the laws that apply to the campaign. Review stricter state rules before using a single nationwide schedule.
Keep message volume consistent with what recipients agreed to receive. Your 10DLC registration supports carrier acceptance; your FCC and TCPA compliance analysis remains a separate responsibility.
How Do You Keep Texting Controls Effective Over Time?
Your texting controls stay effective when you assign recurring checks and document corrective action. Build those tasks into your existing RIA compliance calendar so platform changes and staff turnover receive timely attention.
Train Advisors on Real Client Messaging Scenarios
Use practical training examples drawn from the types of requests your firm handles. Cover scheduling, investment questions, money-movement requests, and texts sent to personal numbers.
Have employees demonstrate the correct response and escalation path. Include an opt-out request and an attachment sent through an unapproved channel.
Train new hires before granting access, then refresh training when your tools or policy change. Keep attendance records and signed acknowledgments with the version of the policy employees received.
Review Messages, Capture Failures, and Policy Exceptions
Use risk-based reviews that reflect your communication volume and business activities. Include relevant checks for misleading claims, unauthorized instructions, and sensitive information.
Monitor capture health separately from message content. A quiet review queue warrants investigation if a connector has stopped sending records.
Log exceptions with an owner, corrective action, and closure evidence. Review repeated off-channel communications for workflow problems as well as employee conduct.
Maintain Evidence and Test Readiness During Quarterly Reviews
Use quarterly reviews to reconcile approved users and business numbers against active capture connections. Sample known conversations and verify that reviewers can retrieve them.
Keep policy versions, consent records, training acknowledgments, review logs, and remediation evidence organized for examination requests. Record the outcome of each retrieval test.
If you need help coordinating those tasks, Secure Wealth IT offers quarterly technology and compliance reviews, audit preparation and evidence collection, and staff cybersecurity training. You can call (704) 769-3663 to request a free compliance readiness assessment, with legal interpretations remaining with your CCO and counsel.
When Do Other Privacy and Marketing Laws Matter?
You need additional legal review when your texting reaches clients in different jurisdictions or involves regulated information. Your obligations follow the facts of the communication and your business activities.
Check State Texting Laws and Cross-Border Client Requirements
Review state laws before launching outreach beyond your established client-service workflow. States differ in their consent standards, covered technology, sending restrictions, and do-not-call provisions.
Record reliable location information and keep it current. A phone number’s area code alone is an unreliable way to determine where your client lives.
For cross-border clients, assess where recipients are located and which services you offer them. Have counsel define the applicable rules before expanding your messaging program.
Distinguish GDPR and PECR Obligations from US Requirements
Assess the General Data Protection Regulation (GDPR) when your activities fall within its territorial scope. Relevant questions include whether you offer services to people in the European Economic Area or monitor their behavior there.
For UK electronic marketing, review the Privacy and Electronic Communications Regulations (PECR) alongside applicable UK data-protection law. EU member states apply their own electronic-marketing rules alongside GDPR.
Document your lawful basis, required marketing permission, and handling of individual rights. Avoid assuming that your US SMS consent form covers these separate duties.
Understand the Limited Relevance of CAN-SPAM and HIPAA
Treat the CAN-SPAM Act primarily as a commercial-email law. The Federal Trade Commission’s commercial-email framework does not provide a complete compliance standard for ordinary SMS.
Review narrow exceptions with counsel if your program involves messages delivered through email-to-phone addressing. Your ordinary texting process still needs its own TCPA and carrier assessment.
Assess HIPAA based on whether your firm acts as a covered entity or business associate in the relevant activity. Receiving health-related information during financial planning alone does not establish that status; protect that information under the privacy and security duties that apply to your firm.
Make Approved Texting Easy to Use and Verify
You can make client texting convenient by giving advisors an approved workflow that your firm can secure, review, and verify. Keep your SMS compliance decisions tied to message content, firm registration, consent, and tested capture coverage.
Start with your inventory of users, numbers, devices, and channels. Have your CCO approve the policy, assign responsibility for text message archiving, and test retrieval before expanding access.
Keep the evidence with your RIA compliance records. At each scheduled review, confirm that current users and numbers remain covered and that any failed capture or policy exception has a documented resolution.
Next Steps for Your RIA or Broker-Dealer Firm
Secure Wealth IT helps Registered Investment Advisors, broker-dealers, and financial advisors stay secure, compliant, and audit-ready. Explore these free tools and resources:
Free Financial Calculators: calculator.securewealthit.com
Compliance Self-Assessment Tool: regulations.securewealthit.com
Resource Library: Browse free RIA and broker-dealer guides.
Watch on YouTube: Secure Wealth IT YouTube channel.
Talk to a Specialist: Schedule a free consultation.
For more information about this topic, visit us at https://www.securewealthit.com

Comments