
EDR vs. MDR: Which Does Your RIA Need in 2026?


Client data sits at the center of every RIA's business. When a threat actor compromises one laptop, the real question is not whether your security tool noticed. It's whether anyone was watching closely enough to stop what happened next.
For most RIAs, the choice between EDR and MDR comes down to one practical question: does your firm have people ready to act on a threat alert at 2 a.m. on a Sunday, or do you need a team that already does? Endpoint Detection and Response (EDR) is software that watches your laptops, servers, and workstations for suspicious activity. Managed Detection and Response (MDR) adds trained analysts who monitor that software around the clock, investigate what it finds, and respond before damage spreads.
Both matter for cybersecurity in regulated industries. Neither one, by itself, guarantees you meet the compliance requirements examiners expect from a modern advisory firm.
Cyber threats aimed at financial firms keep growing more targeted, and regulators have taken notice. Firms considering their next move can start with a conversation about current coverage — Secure Wealth IT offers a free compliance readiness assessment for RIAs weighing exactly this decision.
Key Takeaways:
EDR gives you the technology to detect endpoint threats, but someone still has to watch it, interpret it, and act — every hour of every day.
MDR wraps 24/7 human monitoring, threat hunting, and incident response around your endpoint tools, closing the gap that alerts alone leave open.
The right choice for your RIA depends less on budget and more on whether your team can realistically staff after-hours threat response and produce audit-ready evidence when regulators ask.
What Is EDR and What Does It Protect?

Endpoint Detection and Response (EDR) is software installed on your firm's devices that watches for signs of an attack and can automatically respond to stop it. It focuses on endpoints — the individual devices where your advisors and staff do daily work — rather than your entire network or cloud environment.
EDR platforms record what happens on each device: which programs run, which files change, which network connections open. That record, often called endpoint telemetry, gives security teams a detailed history to review when something looks wrong.
How Endpoint Detection and Response Collects Security Telemetry
EDR agents sit quietly on each device, logging activity in the background. Every process launch, file modification, and outbound connection gets recorded as security telemetry.
That data feeds into a central console where it can be searched and reviewed. Some EDR tools compare activity against known malware databases and lists of indicators of compromise — digital fingerprints tied to previous attacks.
Which Devices Count as Endpoints?
Endpoint devices include laptops, workstations, and servers — the machines advisors and staff use daily, plus the systems that store client records. Many EDR platforms also cover mobile devices used to access firm email or portfolio management tools.
For an RIA, this typically means every advisor laptop, the office desktop workstations, and any server hosting client files or a portfolio management tool like Orion or Tamarac.
How EDR Detects and Contains Suspicious Activity
Modern EDR tools rely on behavioral analysis and machine learning rather than only matching known malware signatures. This lets the software flag unusual patterns — a program suddenly encrypting hundreds of files, for example — even if it has never seen that exact threat before.
When EDR spots something suspicious, it can trigger automated response actions, such as isolating a device from the network. That containment step buys time, but a person still needs to confirm the threat is real and decide what happens next.
What Is MDR and How Does It Work?

Managed Detection and Response (MDR) is a service that pairs your security tools with a team of human analysts who monitor, investigate, and respond to threats around the clock.
Where EDR gives you the recording equipment, MDR gives you the trained staff watching the footage in real time.
MDR providers typically operate what's called a Security Operations Center (SOC) — a dedicated team and set of processes built to catch threats fast and act on them without waiting for someone in your office to notice.
The Role of a 24/7 Security Operations Center
A SOC staffs security analysts in shifts so someone is always watching, including nights, weekends, and holidays. This continuous monitoring matters because attackers often move fastest during the hours a small firm's internal team is offline.
For an RIA with a lean internal IT team, this coverage fills a real staffing gap. Building an in-house team capable of round-the-clock monitoring is expensive and difficult for firms of typical RIA size, which is part of why MDR exists as a service model.
How Security Analysts Triage and Investigate Alerts
Security analysts review incoming alerts, separate real threats from routine noise, and dig into anything that looks serious. This alert triage step is where much of MDR's value shows up, since raw EDR output can include far more notifications than any small team can chase down.
When an analyst confirms a genuine threat, incident investigation begins — tracing what happened, which systems were touched, and how far the activity spread.
What Proactive Threat Hunting Adds
Threat hunting means analysts actively search for signs of compromise instead of waiting for an alert to fire. This proactive work draws on threat intelligence — current knowledge about attacker tactics — to look for subtle warning signs automated tools might miss.
Combined with fast threat response once something is confirmed, this is the operational layer that turns raw detection into a functioning defense.
EDR vs. MDR: The Operational Differences That Matter

EDR is a technology platform you operate yourself; MDR is a managed security service that operates it for you. That distinction shapes cost, staffing needs, and how confidently your firm can respond to an incident at any hour.
Choosing between them, or deciding to combine them as managed EDR, comes down to organizational maturity, risk tolerance, and whether your current team has a real skills gap in security operations.
Technology Platform vs. Managed Security Service
EDR gives you administrative access to a security platform: a console, installation packages, and the ability to export logs for review. Your firm — or your IT team or MSP — owns the job of tuning it, reviewing alerts, and taking action.
MDR functions as an ongoing service relationship. According to Palo Alto Networks' comparison of MDR and EDR, MDR converts the software layer into a managed utility, wrapping human analysis directly around the technology so your firm interacts with an operational partner instead of a dashboard.
Who Owns Monitoring, Escalation, and Containment?
With EDR alone, your internal team or IT provider owns monitoring, escalation decisions, and containment actions. That means someone on staff — or on call — needs to review alerts continuously, including outside business hours.
With MDR, the provider absorbs day-to-day monitoring and initial containment, then escalates confirmed incidents to your team with clear next steps. This shift in ownership is often the single biggest factor RIAs weigh when comparing the two.
Endpoint-Only Data vs. Multi-Source Threat Visibility
EDR sees only what happens on managed devices, which leaves it blind to activity in email, cloud storage, or network infrastructure. MDR providers typically pull in telemetry from multiple sources, giving analysts broader context to spot attacks that never touch a single monitored device directly.
Why Endpoint Alerts Alone Can Leave Gaps
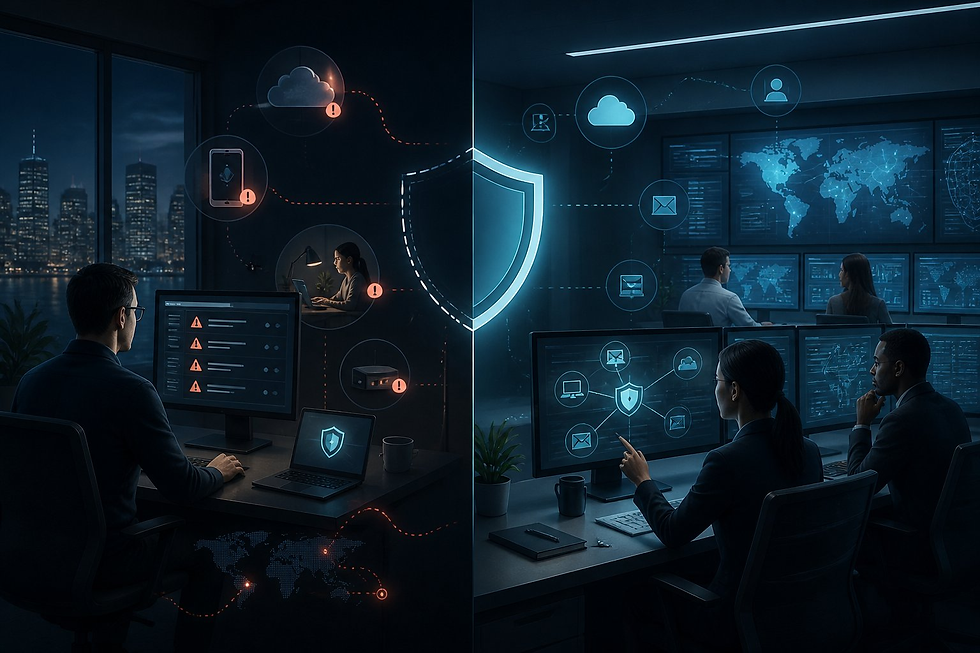
Endpoint alerts alone can miss threats that unfold across email, cloud accounts, or network traffic before ever reaching a monitored device. A firm relying only on EDR — with no one dedicated to reviewing its output — risks missing the alerts that matter most.
Two problems compound this risk: too much noise, and not enough context.
The Operational Cost of Alert Fatigue
EDR tools are tuned to flag marginal anomalies, which generates a high volume of notifications for any human reviewing them. Security teams call this alert fatigue, and it's a documented weakness of unmanaged EDR deployments, since Palo Alto Networks notes that aggressive calibration routinely floods understaffed departments with false positives.
For a small RIA IT team already juggling help desk tickets and vendor coordination, that volume makes it easy to miss the one alert that mattered.
Threats That Require Context Beyond a Single Device
Some of the most damaging attacks, including advanced persistent threats and fileless attacks, are built specifically to avoid tripping endpoint-only detection. Attackers using lateral movement techniques can hop from a compromised email account to a file server without ever triggering a device-level alert in isolation.
Ransomware campaigns frequently start this way, spreading quietly across a network before encrypting files all at once.
Why Automated Isolation Is Not a Complete Response Plan
Automated device isolation stops a threat from spreading further, but it doesn't investigate how the attacker got in or whether client data was accessed. That forensic investigation step requires a person to review logs, confirm the scope of exposure, and document findings — work that matters enormously for compliance requirements and for reporting to your compliance officer.
Without that follow-up, a contained threat can look resolved on the surface while leaving unanswered questions about your attack surface underneath.
How MDR Extends Visibility Beyond Endpoints

MDR extends threat visibility by correlating signals from endpoints, email, identity systems, and network traffic instead of watching devices in isolation. This broader view helps analysts catch attacks that would look harmless if viewed through endpoint data alone.
That correlated approach is especially relevant for RIAs, since client data increasingly lives across cloud platforms, email, and portfolio management tools rather than a single office server.
Correlating Endpoint, Identity, Email, and Network Signals
MDR analysts look at how activity across different systems connects. A suspicious login from an unusual location, paired with unusual file access moments later, tells a clearer story than either signal alone.
This kind of correlation is where firewalls, email security tools, and identity logs earn their value alongside endpoint data.
Monitoring Cloud Workloads and Cloud Environments
Cloud workloads and cloud environments — including Microsoft 365 and Google Workspace accounts — represent a growing share of an RIA's real attack surface. MDR providers often extend monitoring into these environments rather than stopping at the office network's edge.
For firms managing client communications and documents through Microsoft 365, this coverage closes a gap that endpoint-only tools were never built to address.
Where SIEM and XDR Fit Into the Security Stack
A SIEM (Security Information and Event Management) platform aggregates logs from across your systems into one place for analysis. XDR (Extended Detection and Response) goes further, natively integrating telemetry across endpoints, network, cloud, and identity into a single detection engine.
As one comparison of MDR, EDR, and XDR explains, MDR is essentially EDR delivered as a managed service, while XDR represents a technical expansion of what a platform can see in the first place.
Many MDR providers now build their service on top of an XDR-capable platform, combining broader visibility with the human team to act on it.
Why Detection and Response Matters for SEC-
Registered Firms

SEC-registered firms face specific regulatory expectations around protecting client data and demonstrating that protection during an exam. Detection and response capability directly supports both goals, since regulators increasingly ask not just whether a firm has security tools, but whether the firm can show those tools were monitored and acted upon.
Two federal rules shape much of this expectation for RIAs and broker-dealers.
Protecting Client Data and Advisor Communications
SEC Regulation S-P requires firms to safeguard client information, including data handled through advisor communications and portfolio systems. Strong endpoint protection and continuous monitoring support this obligation by reducing the window an attacker has to access sensitive records.
Firms working with broker-dealers should also be aware that FINRA Rule 4370 addresses business continuity planning, which ties directly into how quickly a firm can recover from a security event.
Supporting Evidence Collection After a Security Event
When a data breach happens, examiners and insurers want documented answers: what was accessed, when, and how the firm responded. MDR's incident investigation process naturally produces this kind of evidence, since analysts log their findings as part of confirming and resolving an incident.
Firms that rely only on EDR need a clear internal process for capturing this same documentation, or they risk gaps in their compliance requirements record.
Aligning Security Operations With Cyber Insurance Expectations
Cyber insurance carriers increasingly ask applicants detailed questions about monitoring, response times, and incident history before issuing or renewing a policy. Demonstrating active security monitoring — whether through a mature internal team or an MDR provider — can directly affect underwriting terms.
Secure Wealth IT works specifically with RIAs and broker-dealers on this kind of readiness, aligning security operations with FINRA, SEC, and NIST cybersecurity standards, though no vendor relationship substitutes for a firm's own compliance judgment.
When Is EDR Enough for an RIA?

EDR alone can work for an RIA that already has skilled security personnel monitoring alerts continuously, including outside business hours. This is a narrower situation than many firms assume, since "continuously" is the operative word.
Before deciding EDR is sufficient, it's worth testing that assumption against a few practical questions.
Signs Your Internal Team Can Operate EDR Effectively
A firm is positioned to run EDR internally if it has dedicated security personnel — not just general IT staff — who can review alerts, tune detection rules, and investigate incidents as part of their regular job. This typically describes larger firms with an existing security operations center or a mature managed IT partner filling that role.
If your current setup relies on one generalist IT contact checking a dashboard occasionally, that's a signal that EDR alone leaves a coverage gap.
Questions to Ask About After-Hours Coverage
Ask directly: who reviews EDR alerts overnight and on weekends? What is the actual response time if a critical alert fires at 3 a.m.? A quiet dashboard doesn't mean nothing happened — it may mean no one was watching.
If the honest answer is "no one until Monday morning," that gap deserves attention before an incident forces the conversation.
When Managed EDR May Be a Middle Ground
Managed EDR — where an IT team or MSP takes on monitoring duties without the full scope of an MDR service — can suit small RIAs, sometimes described as SMBs in vendor materials, that want more oversight than a self-managed tool but aren't ready for a full MDR contract.
It's worth confirming exactly which monitoring and response duties are included, since "managed" can mean different things across providers.
When Does an RIA Need MDR?
An RIA needs MDR when it can't reliably staff 24/7 threat monitoring internally, when its cloud footprint and client base have grown past what a lean IT team can watch closely, or when its risk tolerance for a missed after-hours incident is low. These triggers show up gradually, often alongside business growth rather than as a single dramatic event.
Common Triggers for Adding 24/7 Managed Coverage
Firms often add MDR after a near-miss, after a compliance review flags a gap, or simply after recognizing that no one on staff can realistically watch alerts every night. A cyber insurance renewal that asks pointed questions about monitoring capability is another common trigger.
Growing reliance on remote and hybrid work has expanded what needs monitoring, since advisors accessing client data from home networks add complexity beyond the traditional office footprint.
How Growth, Hybrid Work, and Cloud Adoption Change Risk
As an RIA adds advisors, opens satellite offices, or moves more operations into cloud environments, its attack surface grows faster than a small internal team's capacity to watch it. Threat hunting becomes more valuable at this stage, since attackers increasingly probe for weak points in cloud configurations rather than only targeting office devices directly.
What Response Authority Should Be Defined Before an Incident?
Before signing an MDR contract, define exactly what actions the provider can take without waiting for your approval — isolating a device, disabling a compromised account, blocking network traffic. This response authority should be written into the service agreement, not assumed.
Clear escalation paths, including who at your firm gets called and when, prevent confusion during the exact moment speed matters most.
How to Evaluate Providers and Plan the Investment
Evaluate MDR and EDR providers on monitoring scope, response commitments, and reporting quality rather than platform name recognition alone. Two vendors offering "24/7 monitoring" can deliver very different levels of actual coverage once you look closely at contract terms.
Questions to Ask About Monitoring Scope and Response Commitments
Ask what's actually covered: endpoints only, or endpoints plus email, cloud accounts, and network traffic? Ask for a written response time commitment for confirmed incidents, not just alert acknowledgment.
Also confirm whether threat hunting is included or sold as an add-on, since some providers separate this proactive work from standard monitoring.
How to Compare Detection Platforms Without Buying on Brand Alone
Recognizable platforms like CrowdStrike Falcon and SentinelOne offer strong underlying technology, but the platform is only part of the equation. The security operations center and analyst team operating that platform on your behalf determines whether alerts turn into fast, accurate responses.
Factor | EDR (Self-Managed) | MDR (Managed Service) |
Who monitors alerts | Your internal team | Provider's SOC analysts |
Coverage hours | Depends on staffing | 24/7, typically |
Threat hunting included | Rarely | Often included |
Incident investigation | Internal responsibility | Provided as part of service |
Best fit | Firms with dedicated security staff | Firms without 24/7 internal coverage |
Compliance documentation support | Manual process | Often built into service reporting |
What Reporting and Documentation Should an RIA Receive?
Ask for sample incident reports before signing a contract. A strong MDR provider delivers documentation detailed enough to hand directly to an examiner or a cyber insurance underwriter without extensive rework by your compliance team.
Confirm how long records are retained, since some compliance requirements call for multi-year documentation availability.
Selecting Detection and Response Coverage That Fits Your RIA
EDR gives your firm the technology to see what's happening on every device. MDR adds the trained people who watch that technology every hour of every day and act fast when something goes wrong. Most RIAs land on some version of managed detection and response built on strong endpoint detection and response, rather than choosing one over the other entirely.
The right fit depends on your current staffing, your growth trajectory, and how much risk your firm and its compliance officer are comfortable carrying between alerts and action.
A candid look at after-hours coverage, response authority, and documentation practices will point most firms toward their answer faster than a feature-by-feature comparison ever could.
Firms weighing this decision can start with a conversation grounded in their specific compliance requirements and existing security operations, rather than a generic checklist.
Next Steps for Your RIA or Broker-Dealer Firm
Secure Wealth IT helps Registered Investment Advisors, broker-dealers, and financial advisors stay secure, compliant, and audit-ready. Explore these free tools and resources:
Free Financial Calculators: calculator.securewealthit.com
Compliance Self-Assessment Tool: regulations.securewealthit.com
Resource Library: Browse free RIA and broker-dealer guides.
Watch on YouTube: Secure Wealth IT YouTube channel.
Talk to a Specialist: Schedule a free consultation.
For more information about this topic, visit us at https://www.securewealthit.com


Comments